Cybersecurity Track
Practise the response process a SOC analyst runs daily, not just theory
- Wireshark
- Nmap
- Burp Suite
- Splunk
- Kali Linux
- Microsoft Sentinel
- Microsoft Defender
- Metasploit
- Nessus
- OWASP ZAP
- Wazuh
- GitHub
Programme Overview
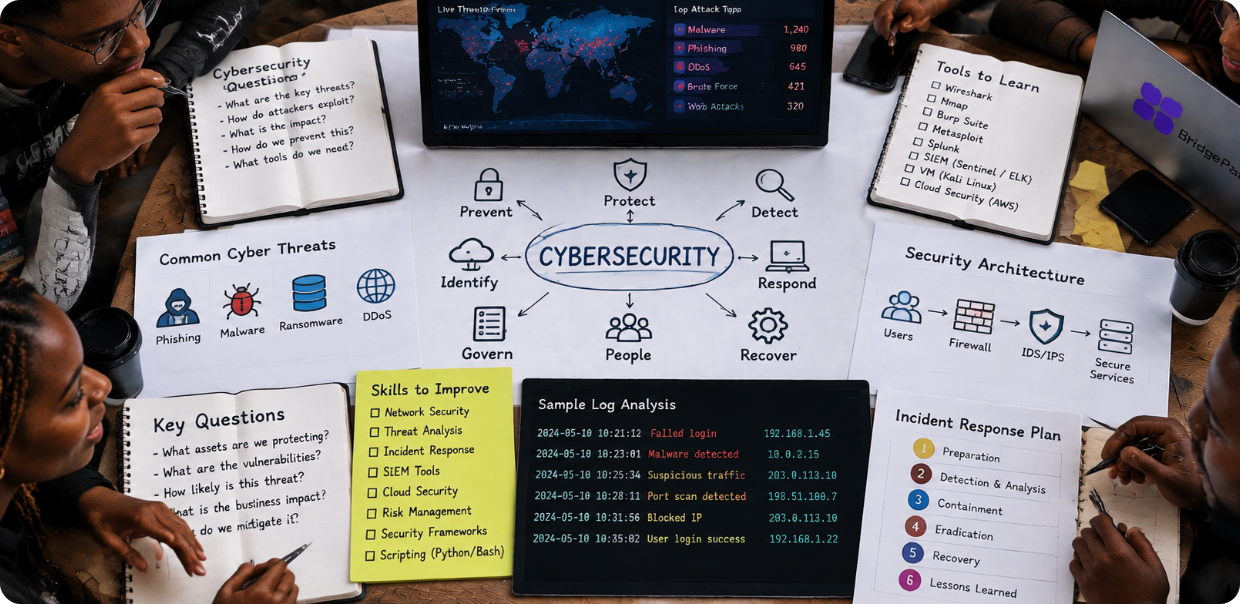
This track puts you inside a simulated security operations team responding to real-feeling incidents, not memorizing a syllabus. Over 12 weeks you complete 4 projects, each anchored to a company scenario in an industry you choose. You will monitor alerts, investigate incidents, and make judgment calls under time pressure, then document your response the way a real SOC analyst would for an audit trail. By the end, you have a documented incident-response history and interview-ready stories about decisions you made under pressure
How you will work at Bridge Path
How your workflow and day-to day looks like at Bridge Path
Your mentor
Opens each project with a briefing video setting the security context and the tools available, and is available for guidance during the project window
AI stakeholder
A simulated persona (for example, a Head of IT Security) escalates the scenario in real time based on how you respond, then reviews your final incident report and challenges your reasoning where relevant
Your Cohort
A shared community channel to compare how others triaged a similar alert or investigated a similar incident, since pattern recognition improves with exposure to more scenarios than your own
Cadence
A monitoring/triage phase, an investigation phase, and a final incident report review at the end of each project
Types of project You Will Build
Below are the types of projects you’ll engage in while at Bridge Path
Incident response
Investigating and containing an active security incident
Monitoring and triage
Sorting real alerts from noise and deciding what deserves escalation
Vulnerability assessment
Identifying weaknesses before they are exploited
Policy and awareness recommendations
Turning a near-miss into a preventative recommendation
Your 4 Projects at Bridge Path
Projects you can choose from
Phishing incident response
A bank is hit by a phishing attack targeting staff credentials. You investigate the scope, contain the incident, and document the response. Deliverable: Incident response report. Skills built: Incident containment, root-cause investigation, response documentation
Security monitoring and triage
A healthcare provider's patient data systems generate a high volume of alerts. You triage them and identify which represent a genuine threat. Deliverable: Triage log plus an escalation recommendation. Skills built: Alert triage, prioritization under volume, SIEM proficiency
Vulnerability assessment
An insurance company's customer portal needs a vulnerability assessment before a planned public launch. Deliverable: Vulnerability assessment report with prioritized fixes. Skills built: Vulnerability scanning and assessment, risk prioritization, remediation recommendations
Security awareness recommendation
A manufacturing company had a near-miss security incident and wants a policy and awareness recommendation to prevent a recurrence. Deliverable: Policy recommendation and staff awareness plan. Skills built: Policy writing, risk communication, preventative thinking
Business Problems You Will Solve
All projects are based on real business problems
Every project is built around a real category of security pressure: an active attack that needs containment, a flood of alerts that needs fast and accurate triage, a system with unknown weaknesses before a launch, or an organization that got lucky once and needs to make sure it does not happen again. These are exactly the situations a hiring manager expects an entry-level SOC candidate to demonstrate sound judgment on
Industries You Can Choose From
Pick up to 4 for your internship
Fintech & Digital Banking
Investigate suspicious activity across a digital bank's payment systems and identify the security gaps that could expose customers to fraud
Manufacturing & Industrial
Investigate unusual activity across a manufacturing plant's operational systems and identify cybersecurity gaps that could disrupt production or compromise industrial assets
Public Sector & GovTech
Investigate unauthorized access to a government service portal and identify the security gaps putting citizen data at risk
Telecommunication
Investigate unusual activity across a telecom network and identify the vulnerabilities that could enable account takeovers and unauthorized access
Healthcare and Healthtech
Investigate a potential breach of a health platform and identify the security gaps that could expose sensitive patient information
Insurance
Investigate suspicious access to an insurance claims system and identify the vulnerabilities that could enable fraud or unauthorized data access
Job Market Intelligence
Financial services, healthcare, and government/public sector are currently the strongest hirers of remote cybersecurity talent across the UK, US, and Canada, with financial services generally offering the highest remote salary bands
What You Walk Away With
By the end of your journey with us, you’ll achieve the following:
Achievement 1
4 documented incident-response and assessment reports
Achievement 2
A CV rebuilt around this specific experience gained
Achievement 3
4 STAR-format interview statements, one per project
Achievement 4
A LinkedIn profile positioned around demonstrated, scenario-based security judgment
Frequently Asked Questions
Below are some of the questions we receieve very often